Is the encryption function in the RSA cipher an exponential function modulo n and the decryption function an exponential function with a different exponent?
The RSA cryptosystem is a foundational public-key cryptographic scheme based on number-theoretic principles, specifically relying on the mathematical hardness of factoring large composite numbers. When examining the encryption and decryption functions in RSA, it is both accurate and instructive to characterize these operations as modular exponentiations, each employing a distinct exponent.
Key Generation in RSA
The RSA algorithm begins with the generation of two large prime numbers, denoted as  and
 , which are kept secret. Their product
 forms the modulus for both the public and private keys. The totient (Euler’s phi function) of
 is computed as
 . The public exponent
 is chosen such that
 and
 , ensuring that is invertible modulo
 . The private exponent
 is then computed as the modular multiplicative inverse of modulo , satisfying
 .
– Public key: 
– Private key: 
Encryption Function
Given a plaintext message  , where
 , the encryption operation transforms into ciphertext
 using the recipient's public key:

This is unequivocally an exponential function, where the base is the message and the exponent is the public key exponent , all computed modulo . The operation is performed in the mathematical group of integers modulo , denoted as  .
Decryption Function
To recover the original message from the ciphertext , the recipient uses the private key exponent :

Again, the decryption function is an exponential function modulo , this time with the ciphertext as the base and the private exponent as the exponent. The operation takes advantage of the modular arithmetic properties and the mathematical relationship between and .
Why Modular Exponentiation?
The use of modular exponentiation is no accident. The core of RSA's security and correctness is rooted in Euler’s theorem, which states that for any integer  coprime to :

Since , there exists an integer  such that
 . Therefore, decryption undoes encryption, as shown below:

Since  , this simplifies to .
Didactic Example
Let us consider a concrete example using small primes for clarity (note: in practice, primes must be hundreds of digits for security):
1. Choose primes:  ,
 .
2. Compute  .
3. Compute  .
4. Choose  (commonly used, coprime to 3120).
5. Compute such that 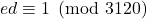 . Here,
 .
Suppose Alice wishes to encrypt  for Bob:
– Encryption:

– Decryption:

Both operations are modular exponentiations; encryption uses exponent 17, decryption uses exponent 2753, both modulo 3233.
Efficient Exponentiation
In practical implementations, computing  or
 directly by performing exponentiation then reducing modulo would be computationally infeasible for large exponents. Instead, algorithms such as "square-and-multiply" (also known as binary exponentiation) are used. These algorithms break down the exponentiation into a sequence of squarings and multiplications, each followed by a modular reduction, which enables efficient computation even for very large exponents and moduli.
Mathematical Properties Ensuring Correctness
The correctness of RSA depends on the following properties:
– The mapping  is injective (one-to-one) on the set of valid messages, provided is coprime to .
– The inverse mapping 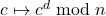 recovers the original message , owing to the relationship .
– The security of RSA is predicated on the difficulty of deducing from and , or equivalently, factoring to find and , which then enables computation of .
Theoretical Underpinnings
The algebraic structure underlying RSA is the multiplicative group of integers modulo , denoted as  . For messages that are not coprime to , certain technical adjustments are made, but in typical circumstances, messages are required or padded to ensure coprimality.
From group theory, the modular exponentiation function is a group automorphism when restricted to . This automorphism is invertible, with the inverse map given by exponentiation to the power .
Summary of the Functions
– Encryption function: Exponential function modulo with exponent :  .
– Decryption function: Exponential function modulo with exponent :  .
Both processes are mathematically equivalent to raising the input to a power (either or ) and reducing the result modulo .
Potential Pitfalls and Security Considerations
It is important to note that textbook RSA (as described above) is deterministic and malleable; that is, encrypting the same message twice yields identical ciphertexts, and certain algebraic manipulations on ciphertexts translate into predictable changes in the plaintext. For these reasons, practical deployments use padding schemes (such as PKCS#1 v1.5 or OAEP), which randomize the plaintext before encryption, thus greatly enhancing security.
Additionally, if improper values are chosen for or if the primes and are too small or poorly generated, the RSA system can be compromised. The exponents must be large enough to prevent certain attacks but small enough to allow efficient computation.
The encryption and decryption functions in RSA are both modular exponentiation operations, differing solely in the exponent used—public exponent for encryption, private exponent for decryption. The mathematical symmetry and invertibility of these functions are central to the operation and security of the RSA cryptosystem.
Other recent questions and answers regarding The RSA cryptosystem and efficient exponentiation:
- Was public-key cryptography introduced for use in encryption?
- In RSA cipher, does Alice need Bob’s public key to encrypt a message to Bob?
- How many part does a public and private key has in RSA cipher
- What is the exponentiation function in the RSA cipher?
- Are public keys transferred secretly in RSA?
- How many keys are used by the RSA cryptosystem?
- In the context of public-key cryptography, how do the roles of the public key and private key differ in the RSA cryptosystem, and why is it important that the private key remains confidential?
- Why is the security of the RSA cryptosystem dependent on the difficulty of factoring large composite numbers, and how does this influence the recommended key sizes?
- How does the method of "Exponentiation by Squaring" optimize the process of modular exponentiation in RSA, and what are the key steps of this algorithm?
- What are the steps involved in the key generation process of the RSA cryptosystem, and why is the selection of large prime numbers crucial?
View more questions and answers in The RSA cryptosystem and efficient exponentiation